Self-service Defender onboarding
A wrapper on a shared folder that let support teams onboard devices, logging who ran it, when and with what rights.
Endpoint security and control assurance specialist. Six years inside a bank operating in seven countries, running SentinelOne, Microsoft Defender and Zscaler through growth, migration and audit. CISM and CIPP/E certified.
Available at short notice. Saudi work visa held; relocating to Riyadh.Work I did at the bank, rebuilt on fictional data.
At the bank I built a workbook by hand that joined ten security tools against the asset inventory, to answer one question: which devices are actually protected? This is that design rebuilt on fictional data, with an interactive dashboard and the ten defects I found and fixed in my original.
Open the case studyFictional 1,500-device estate.
After each rollout (Defender, SentinelOne, Darktrace, Zscaler) I wrote a scoped assessment and a printed checklist where every check had an owner, evidence and a manager's signature. Try the Defender version.
Open the checklistThe step-by-step method I used before escalating EDR cases to the vendor, from name resolution to certificates, with the real incidents that shaped each check.
Walk through the runbookScripts and processes from the day-to-day work, reconstructed with placeholders.
One pass over every security agent on a device: SentinelOne, Defender, Zscaler, Trend Micro, ManageEngine, Forescout, Lansweeper and DLP, with deeper checks where a running service is not proof of protection.
See the script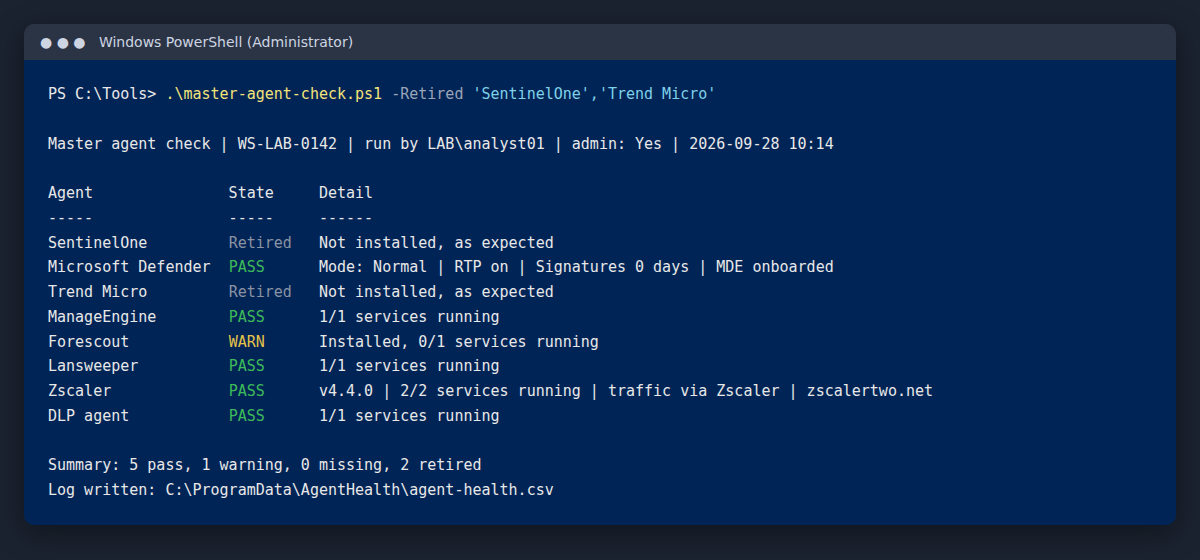
A wrapper on a shared folder that let support teams onboard devices, logging who ran it, when and with what rights.
How a deletion request moved from ticket to approval to BigID, and why I closed on a rescan, not a screenshot.
The seven checks that turned vendor escalations into evidence-backed cases.
Frameworks I have studied and modelled end to end on fictional data, built with AI assistance while preparing for governance and assurance roles. They show how I would structure the work, not experience I am claiming.
Evidence register mapped to PCI DSS v4.0.1 across endpoint and malware, vulnerability remediation, access and MFA, logging and incident response. Closest to the audit support I did at the bank.
All 93 Annex A controls with a gap matrix, risk register, treatment plan and corrective actions, rolled up into an executive dashboard.
Record of processing activities and a DSAR tracker with statutory deadlines under GDPR and GCC data protection laws.
Executive, operations and risk dashboards covering control coverage, patch latency, vulnerabilities, EDR health and incident SLAs.
Executive reports, timelines, root-cause analysis and corrective actions tracked through to effectiveness checks.
Detection rules mapped to MITRE ATT&CK, alert triage notes, false-positive handling and tuning.
Sample DLP policies with exception workflow, alert triage, governance and a KPI/KRI dashboard.
Defender onboarding lagged behind target. I split the gap by cause and cleared each list with the team that owned it.
Won central bank and risk-committee sign-off by answering data retention and deletion questions in writing.
About 450 agents dropped offline on an expired certificate. I renewed it, then made expiry alerts a team responsibility.
A phishing payload tried to switch off antivirus. The device was quarantined before damage was done.
I refused a request to keep EDR disabled during a file transfer and explained which controls would catch it.
Rebuilding my workbook, I found ten defects, including drifting lookups. The public version fixes all of them.
B.Sc., University of the Punjab, 2007. English (professional), Urdu (native), Arabic (basic).
mohsin_sharif1@outlook.com
+973 3447 9797 (WhatsApp)
LinkedIn profile GitHub
Download my CV: standard version (PDF) | executive profile (PDF). Versions tailored for security delivery, IT risk or privacy roles are available on request.